Troubleshoot unknown or bad certificates or certificate authorities
Enable logging for TLS/SSL decryption rules to monitor connection events and identify certificate-related issues. This helps you diagnose problems with certificate authorities, bad certificates, or unknown certificates in your TLS/SSL connections.
You can view connection events to determine whether or not the devices are experiencing unknown certificate authorities, bad certificates, or unknown certificates. This procedure can also be used if a TLS/SSL certificate has been pinned. You must add at least the and TLS Flow Messages columns to the table view of events.
Before you begin
-
Set up a decryption rule.
-
Enable logging for your decryption rules as discussed in the section on logging decryptable connections in decryption rules in the Secure Firewall Management Center and Threat Defense Management Network Administration guide.
Follow these steps to troubleshoot unknown or bad certificates or certificate authorities:
Procedure
Step 1 | Click . | ||||||||
Step 2 | In the table view, click the Column set icon and select the required columns. 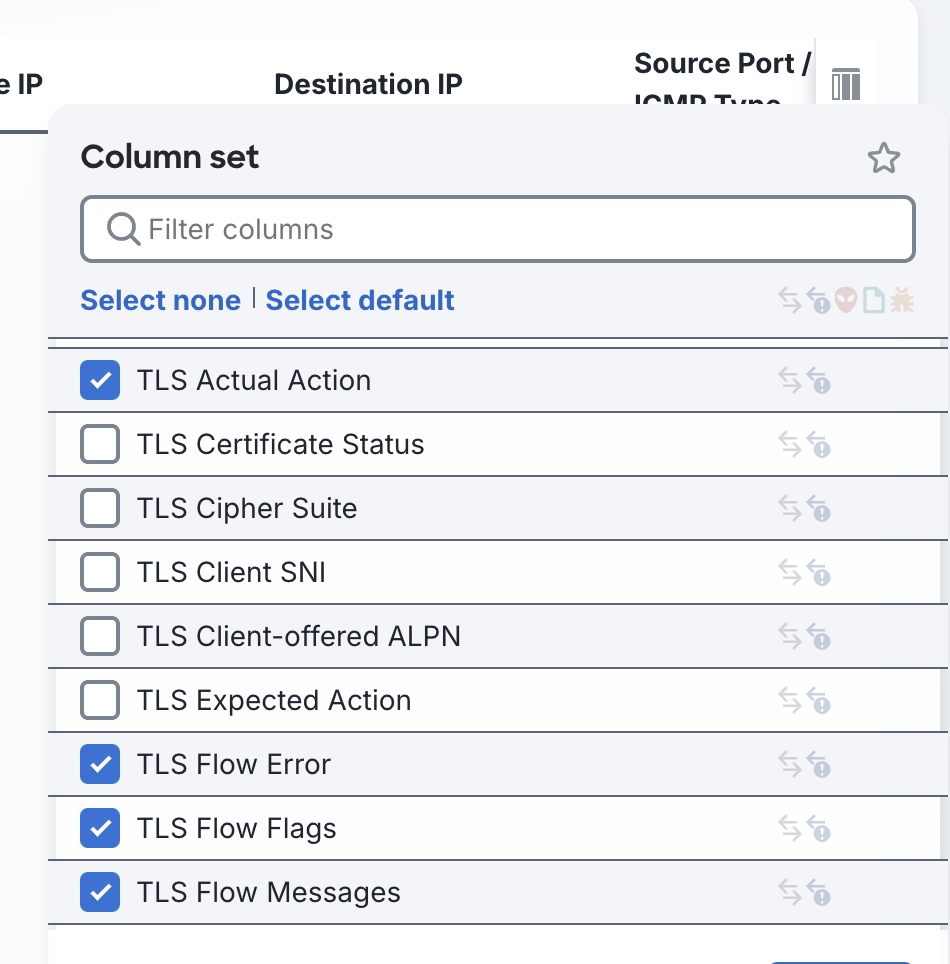 | ||||||||
Step 3 | Click Apply. | ||||||||
Step 4 | Review the SSL flow flags to determine if a certificate or certificate authority is bad or missing.
|